Continuous Monitoring in Cybersecurity: Real-Time Assurance for Changing Risk
By BCyber Security Team | CISSP, CISM Last updated: 20 September 2026

Most organisations still review security through periodic checkpoints: a monthly report, a quarterly risk meeting, or an annual audit cycle. That approach can show what was true at a moment in time, but it rarely tells you what changed an hour later. In a live environment, control failures, access changes, and risky behaviour can emerge between meetings and stay hidden until the next review. Continuous monitoring closes that gap by turning security evidence into an ongoing source of assurance, not a retrospective record.
For organisations operating under the Privacy Act 1988, APRA CPS 234, the Essential Eight, or ISO-aligned assurance programs, that difference is not academic. It is the difference between “we believe the control worked” and “we can show it worked, today, with evidence.”
Why periodic checks no longer tell the full story
Cybersecurity used to fit neatly into scheduled cycles, but modern environments move too quickly for that rhythm alone. Cloud workloads scale up and down, identities change hands, vendors connect and disconnect, and user behaviour shifts with every new business process. A control that was sound on Monday may be misconfigured by Wednesday, and a privileged account that looked harmless last week may become a live exposure after a role change.
That is why the old question, “Did we pass the review?”, is being replaced by a more useful one: “Do we know what changed since the review?”
Continuous monitoring matters because it gives governance teams, security operators, and executives a shared view of the living environment. It is not just about spotting threats faster, though that matters; it is also about seeing whether controls are still behaving as designed. For Australian organisations, that visibility supports practical obligations under the Privacy Act 1988, APRA CPS 234, the Essential Eight, and sector-specific resilience expectations.
A practical example: in a financial services environment, an external identity provider may be updated overnight, changing authentication behaviour for a privileged admin group. If the organisation is only checking access recertification monthly, the drift may persist long enough to become an exposure. Continuous monitoring catches the change closer to the event and supports a faster control decision.
If your control environment changed this morning, would you know before the next board pack or assurance review?

What continuous monitoring actually means
A working definition of continuous monitoring
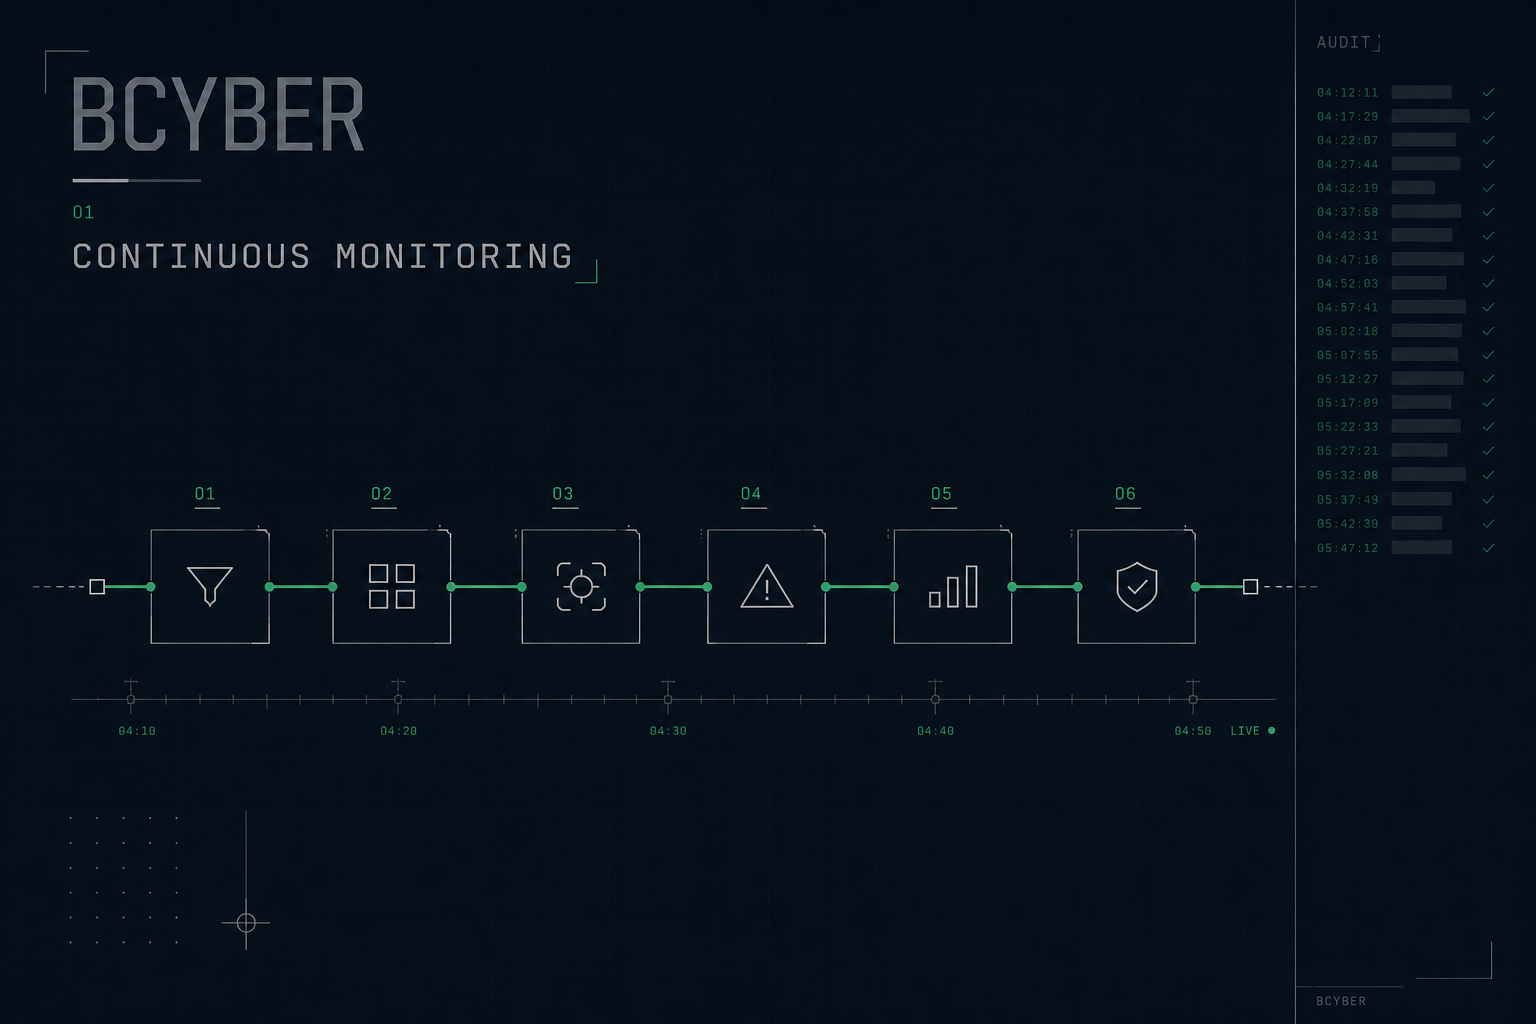
Continuous monitoring is the ongoing collection, analysis, and actioning of security evidence so an organisation can see changes in control effectiveness, risk posture, and threat activity as they happen. The word “continuous” does not always mean every second, and it does not require a noisy stream of alerts for the sake of activity. It means the organisation has a monitoring rhythm that is current enough to support timely decisions, timely escalation, and timely correction.
In practice, that could involve minute-by-minute telemetry for some systems, daily assurance checks for others, and event-driven monitoring where the risk warrants it. For example, a government shared-services platform may monitor privileged role changes in near real time, while a low-risk internal process may only require daily verification of backup completion. The cadence should match the control objective and risk appetite.
What makes the discipline useful is not the volume of data, but the quality of the question being asked. Are privileged accounts changing in ways that match approved access rules? Are backups actually completing and restoring? Are cloud settings drifting from the approved baseline? Are privacy controls still aligned to how data is being collected, shared, and retained?
Those questions turn monitoring into assurance, because they connect technical signals to business consequences.
How it differs from traditional monitoring
Traditional monitoring is often manual, isolated, and reactive. A team checks a report, a spreadsheet is updated, a ticket is raised, and the cycle repeats when someone remembers to look again. That model can work for low-churn environments, but it struggles when identity, cloud, endpoints, and third parties all change at once. It also tends to keep each function in its own lane, which means the security team sees one part of the story while compliance or risk sees another.
Continuous monitoring is more connected and more responsive. It uses automated or semi-automated checks where possible, correlates data across domains, and highlights changes that matter rather than every event that occurred. The difference is subtle in description but significant in effect: traditional monitoring says “something happened”; continuous monitoring says “this changed, here is why it matters, and here is what should happen next.”
This aligns well with control environments mapped to ISO/IEC 27001:2022, where ongoing performance evaluation, internal audit, and management review depend on evidence quality. It also aligns with the NIST Cybersecurity Framework functions of Detect, Respond, and Recover, particularly where organisations need reliable telemetry to evidence control effectiveness over time.
Why it belongs in assurance, not only in operations
Security operations wants to detect and respond, which is necessary. Assurance wants to prove that controls are working over time, which is equally necessary, but often overlooked. Continuous monitoring supports both because it produces evidence that can be used for incident response, control validation, audit readiness, and board reporting. It becomes a living feedback loop rather than a static control register.
That matters because assurance is not just about compliance paperwork; it is about whether the organisation can demonstrate control health with evidence that stands up to scrutiny. If a control is meant to prevent, detect, or correct risk, then the organisation should be able to show whether it is actually doing so.
BCyber’s assurance approach reflects that operating model through the GRACE Portal (Unified Cyber Resilience Platform), which provides a single dashboard, cross-product analytics, executive reporting, compliance tracking, and real-time monitoring. In practice, that means monitoring evidence is not left scattered across separate tools and spreadsheets; it can be reviewed as part of a connected assurance loop.
Why continuous monitoring changes decision-making
Faster detection of control failures
Control failures rarely arrive with a warning label. A misconfigured storage bucket, an expired certificate, a dormant privileged account, or a failed backup job can sit quietly until the environment changes enough to expose the weakness. Continuous monitoring shortens that blind period by surfacing the issue closer to the point of change. That matters because the earlier a failure is detected, the more options the organisation usually has for correction.
Consider a healthcare provider where access to electronic medical records is temporarily granted to a contractor for a clinical systems upgrade. If monitoring is periodic, access may remain active well past the project end date before anyone notices. If the monitoring loop is continuous, the exception can be spotted, validated, and remediated before it becomes normalised. In healthcare, that is not just a technical issue; it is a privacy, governance, and patient-trust issue.
The same logic applies to patching gaps, policy violations, and control drift: early visibility creates room to act while the problem is still small.
Better risk awareness across changing conditions
Risk is not a static score written once into a register. It changes when a vendor relationship changes, when a new SaaS platform is introduced, when staff move roles, or when threat activity shifts against a particular sector. Continuous monitoring keeps the risk picture aligned to those moving parts by feeding fresh evidence into the decision process. That makes prioritisation more realistic because attention is focused where the environment is actually changing.
This is especially important in Australian organisations that need to show how risk is being managed across governance, privacy, and operational resilience. A risk register is only useful if it reflects current conditions, and a control assessment only matters if it is anchored to evidence rather than assumption. Continuous monitoring makes that possible by connecting signals from identity, endpoints, cloud, and compliance records into a more complete picture.
BCyber’s Paradigm (AI Self-Learning GRC Platform) is designed for this kind of control-to-risk linkage. Its Synapse AI Engine supports continuous self-learning posture management, risk quantification, policy automation, and compliance mapping. That makes it especially relevant for organisations managing recurring obligations under APRA CPS 234, internal control attestations, and privacy obligations under the Privacy Act 1988.
Stronger incident response and containment
A faster signal is useful only if it leads somewhere. Continuous monitoring supports incident response because it feeds detection data directly into investigation and escalation workflows. If a login pattern looks unusual, if an endpoint begins behaving oddly, or if data is accessed outside expected hours, the response team can act before the event spreads. That can reduce dwell time, limit operational disruption, and improve containment.
This is where monitoring and response should be tightly linked. BCyber’s CyberTriage (AI-Powered Incident Response) is designed for 4-minute triage, automated response, threat containment, forensic analysis, and incident playbooks. In operational terms, that means a suspicious event discovered by monitoring can move into validated triage without waiting for manual queueing or fragmented hand-offs.
For example, a government agency may detect a privileged account login from an unusual geo-location outside expected business hours. Continuous monitoring can flag the deviation, while triage workflows can validate the event against known travel, token usage, and access policy exceptions. The result is a faster and better-informed response.
Clearer executive and board reporting
Boards and executives do not need a flood of technical detail; they need reliable evidence of what has changed, why it matters, and what is being done. Continuous monitoring enables that kind of reporting because the data is already current, traceable, and trend-aware. Instead of asking whether a control was tested sometime this quarter, leadership can see whether it is holding, where exceptions are rising, and which risks are being actively managed.
That makes the conversation more strategic and less speculative. For assurance functions, it also creates reporting that is based on observed control performance, not just self-attestation. It helps explain where resources should be directed, because trends reveal whether a control weakness is isolated or recurring.
BCyber’s platform ecosystem supports this through the GRACE Portal, with cross-product analytics and executive reporting that can incorporate data from Profiler for behavioural intelligence, Paradigm for GRC posture, and CyberTriage for incident findings. In a mature program, that gives leaders a clearer line of sight from technical evidence to board-level assurance.
Building a monitoring loop that actually works
Data collection from the right sources
A useful continuous monitoring program starts with evidence, not with dashboards. The organisation needs to collect security-relevant data from systems that reflect how the business actually operates, including identity and access management, endpoint telemetry, cloud configurations, vulnerability scanners, incident logs, privacy records, and policy systems. If the data sources are too narrow, the program will look impressive but miss the changes that matter. If they are too broad without structure, the team will drown in noise.
The best approach is to begin with the most critical assets and controls, then expand outward. For example, a financial services organisation may prioritise privileged access reviews, transaction anomaly monitoring, and third-party connectivity before moving into broader behavioural analytics. A healthcare provider may prioritise patient record access, backup status, and privileged account review before moving into broader behavioural analytics. A government agency may focus first on administrative access, configuration drift, and evidence of control operation across essential services.
BCyber’s Profiler (Behavioral Intelligence Platform) is particularly relevant here because it supports behavioral analysis, insider threat detection, access pattern monitoring, risk scoring, and user activity analytics. That makes it useful where the monitoring requirement is not just “is the system up?” but “is the way people are using the system consistent with approved control expectations?”
Analysis that turns raw signals into evidence
Raw telemetry is not yet assurance. It becomes useful when it is analysed, correlated, and interpreted in context. That means looking for patterns, exceptions, and trends across systems rather than treating each alert as an isolated event. A single login attempt may mean little on its own, but paired with a new device, unusual geography, and a privilege escalation, it becomes a materially different signal.
This is where cross-functional correlation matters. A privacy event might be relevant to risk management, an endpoint alert might matter to governance, and a failed patch might be relevant to resilience. If those signals remain in separate tools and separate teams, the organisation loses the chance to understand the combined effect. Continuous monitoring works best when the system can relate one signal to another and show how they connect.
That approach is also consistent with NIST SP 800-137 on Information Security Continuous Monitoring, which emphasises ongoing assessment, change monitoring, and status reporting as part of the security lifecycle.
Alerting, prioritisation, and human judgement
Not every monitored event deserves the same response. If everything is urgent, nothing is urgent, and alert fatigue quickly erodes trust in the system. Effective monitoring uses risk-based thresholds so that high-value signals rise first and lower-priority events are queued, grouped, or summarised appropriately. The goal is not to create more alerts; it is to make the right alerts visible at the right time.
Human judgment still matters here. Automated monitoring can surface patterns and exceptions, but people must decide what is material, what is noise, and what needs escalation. That is why BCyber’s approach to operative intelligence is best understood as human-on-the-loop rather than fully autonomous. The system can learn, surface, and adapt, but it should also admit what it cannot yet determine and leave room for expert review where the context is ambiguous.
For teams seeking formal capability uplift, BCyber’s training library includes courses such as Continuous Monitoring, GRC Foundations, Incident Response, and Privacy in Depth. These align particularly well to GRACE-style assurance workflows because they reinforce the relationship between monitoring evidence, policy obligations, and reporting discipline.
Response, remediation, and reporting
Monitoring without response is just observation. Once an issue is detected, the organisation needs defined workflows for investigation, escalation, remediation, and reporting. Those workflows should link to the control owner, the risk owner, and the business stakeholder who can make the decision or approve the fix. If the response path is unclear, the value of monitoring drops quickly because the issue is seen but not resolved.
A practical program closes the loop by feeding outcomes back into the system. If the alert was a false positive, the threshold can be refined. If the issue was real, the control can be adjusted, the risk register updated, and the reporting layer informed. That is how monitoring becomes a learning system rather than a reporting exercise. Over time, the evidence base should get sharper, not just larger.
How continuous monitoring spans the whole organisation
Governance, privacy, and resilience in one loop
Continuous monitoring should not sit only in the security team. Governance needs visibility into whether decisions are implemented, risk needs evidence that control changes are reflected in the register, privacy needs assurance that data handling remains within policy, and resilience needs proof that recovery controls still work. When these functions operate together, the organisation gets a clearer view of whether it is actually prepared. When they stay siloed, each team may have part of the answer and none of the full picture.
That connected view is particularly useful when incidents cut across domains. A suspicious account may trigger a technical response, but it may also require a privacy review, a risk update, and an executive note. In a mature operating model, those downstream actions do not depend on someone remembering to notify the right team. They happen because the monitoring loop has been designed to propagate evidence where it is needed.
This is one reason BCyber’s ecosystem is structured around integrated capabilities rather than standalone tools. GRACE Portal provides the central control view; Paradigm manages GRC workflows; Profiler captures behavioural signals; CyberTriage accelerates incident response; and Perfect Storm (Scenario Intelligence) supports scenario modelling, threat simulation, impact analysis, resilience testing, and war gaming. Together, these capabilities support assurance from multiple angles rather than relying on a single checklist.
User behaviour and control drift
Many control issues start with people, not machines. An employee may access data in a way that does not match their role, a contractor may keep access too long, or a privileged user may take an action outside established patterns. Continuous monitoring can help spot those changes early through behavioural analysis and policy-based checks. That does not mean treating every deviation as malicious, but it does mean noticing when behaviour no longer fits the expected control environment.
Control drift is another quiet risk. A policy may still exist on paper while the actual process has changed around it. A backup job may still be listed as active while its recovery path is no longer tested. Continuous monitoring gives organisations a practical way to see whether the operating reality still matches the documented control.
BCyber’s platform inventory shows this emphasis on operational assurance at scale: 23 policies, 9 processes, 50 courses, 937 published articles, 519 knowledge hub entries, 10 clients, and 14 fact-find assessments. These figures are provided for contextual transparency and should be interpreted as platform-disclosed data rather than independently audited market statistics.
Common pitfalls and the habits that keep monitoring useful
Where programs usually go wrong
The most common mistake is collecting too much data and turning too little of it into action. Another is buying tools that produce dashboards but do not connect to ownership, remediation, or reporting. Some organisations also assume that once monitoring is configured, the work is done, when in reality the environment, thresholds, and risk priorities keep changing. Those gaps create a false sense of coverage that can be more dangerous than having no monitoring at all.
A further trap is trying to monitor everything equally. That usually leads to noisy outputs, frustrated analysts, and weak executive attention. A better approach is to start with the controls and assets that matter most, define what “normal” looks like, and then tune the system around actual risk. This is where the model becomes self-learning: each review improves the next one, and the monitoring loop becomes more precise over time.
Practices that make the program durable
A durable program is built around a few habits that are easy to describe and hard to sustain unless they are deliberate. It should prioritise critical controls first, use risk-based thresholds, and link each alert to a clear owner and response path. It should also review reporting regularly so that executives see concise evidence, not technical clutter. Most importantly, it should be treated as a living capability rather than a one-off implementation.
Useful practices include:
- starting with the highest-risk systems and controls
- defining clear escalation criteria
- mapping alerts to remediation owners
- correlating evidence across multiple sources
- reviewing thresholds after incidents and near misses
- keeping executive reports short, current, and decision-focused
Those habits do not remove complexity, but they make the complexity manageable. They also help the program compound, because each cycle teaches the next one something useful. That is the difference between a monitor that watches and a monitor that improves.
GRACE Portal and connected assurance in practice
Why a single dashboard matters
Continuous monitoring becomes far easier to manage when evidence is brought into one place. A single dashboard does not solve every problem, but it gives teams a shared view of the current state, the open exceptions, and the trends that matter. For security teams, that reduces friction. For risk and governance teams, it makes oversight more practical. For executives, it creates a clearer line of sight from technical evidence to business assurance.
BCyber’s GRACE Portal is designed around that connected model. Its value is not simply that it stores information, but that it helps connect monitoring, analytics, and reporting into one operational loop. That matters because evidence fragmented across tools is harder to interpret and easier to ignore. When the evidence is assembled into a coherent view, the organisation can see where controls are holding, where they are drifting, and where attention is needed next.
Cross-product analytics and reporting
Cross-product analytics become especially useful when different tools are seeing different parts of the same story. One system may flag a control exception, another may record a related identity change, and a third may show that the remediation task is overdue. If those signals are analysed together, the organisation can move from isolated observations to a more complete assurance view. That is what turns monitoring into something operationally useful rather than merely informative.
Executive reporting also becomes simpler when the underlying evidence is already structured. A board-ready summary can show the status of critical controls, exceptions that need attention, and trends that indicate whether risk is improving or worsening. It can also distinguish between issues that are known, issues that are being remediated, and areas where the evidence is still incomplete. That level of honesty is useful because it tells leaders what is real, not just what looks tidy.
BCyber recognition and authority context
BCyber’s work in this space is informed by both practitioner delivery and industry recognition, including:
- 2025 Finalist Cybersecurity Professional Of The Year — Karen Stephens, Co-Founder & CEO
- 2025 GRC Provider of the Year — Finalist
- 2025 AI Innovator - Cyber Security — Finalist
These recognitions are included here to provide context on market visibility and domain focus. They are not, by themselves, proof of technical suitability for every environment; they should be considered alongside architecture fit, control requirements, and assurance evidence.
Key Takeaways
Continuous monitoring gives organisations a way to see security and control changes while they are still relevant, not weeks after the fact. It shifts assurance from periodic review to an ongoing feedback loop that connects evidence, analysis, response, and reporting. It also helps align governance, risk, incident response, privacy, and resilience so the organisation is not making decisions from fragmented views.
For Australian organisations, that connected evidence can support obligations under the Privacy Act 1988, APRA CPS 234, and the Essential Eight in a way that is practical and reviewable. The most important question is still the simplest one: would you know today if your control environment changed this morning?
Authoritative references
For further reading, see:
- APRA CPS 234 — Information Security
- ACSC Essential Eight Maturity Model
- NIST SP 800-137 — Information Security Continuous Monitoring (ISCM) for Federal Information Systems and Organizations
- NIST Cybersecurity Framework 2.0
- ISO/IEC 27001:2022 overview
- OAIC — Australian Privacy Principles
- ACSC Guidance — Implementing the Essential Eight
Verification note: BCyber platform figures referenced above are based on current platform-reported data supplied for this article. Where statistics or product capabilities are mentioned, they should be validated against current internal records, client documentation, and applicable regulatory guidance before publication or procurement decisions.
Potential bias disclosure: This article references BCyber products and services because the request supplied BCyber platform data and asked for authority citations. Readers should evaluate vendor claims in the context of their own control environment, independent assurance, and procurement requirements.