CISO Strategy and Leadership: Building a Business-Aligned Cybersecurity Function for Resilience, Growth, and Trust

By BCyber Security Team | CISSP, CISM Last updated: 3 August 2026
Cybersecurity is no longer a background technical service that quietly supports the business from the sidelines. It is now a leadership discipline that shapes risk, resilience, compliance, and trust across the enterprise. The modern CISO must translate technical exposure into business language, guide investment decisions, and help executives choose the right trade-offs under pressure.
In practice, that means security strategy must be evidence-based, business-aligned, and capable of adapting as the organisation changes. At BCyber, this is reinforced by our proof not promises approach and by real delivery evidence across the BCyber REAL platform data set: 21 policies, 8 processes, 50 courses, 773 published articles, 374 knowledge hub entries, 11 fact-find assessments, and 9 clients.
Verification note: Operational statistics in this paper are drawn from BCyber platform records available at the time of publication and may change as programs, assessments, and content libraries are updated.
The CISO’s Expanding Mandate in a Connected Enterprise
From technical defender to business leader
The CISO role has shifted far beyond monitoring alerts and coordinating incident response. Today, the CISO is expected to understand business priorities, critical services, and the financial consequences of disruption. That requires more than technical skill; it requires judgment, communication, and the ability to frame cyber risk as enterprise risk.
A strong CISO does not simply ask whether a control is deployed, but whether the control meaningfully reduces business exposure. This is where cybersecurity becomes part of management, not just operations. In a financial services environment, for example, a payment platform outage is not just an availability issue; it can trigger liquidity pressure, customer churn, operational losses, and potential APRA reporting obligations.
That shift is especially important in organisations navigating cloud migration, SaaS adoption, and hybrid work. Security teams can no longer assume a stable perimeter or a fixed set of assets. Identities, data, and access pathways now move across environments, vendors, and user contexts with constant motion. The CISO must therefore lead with a broader lens, focusing on the services the business cannot afford to lose.
In that model, the question changes from “What is the latest threat?” to “What would materially interrupt the organisation if that threat succeeded?” That is a leadership question, not just a technical one.
Why strategy matters more as threats evolve
Threat actors increasingly target identity, cloud services, third-party relationships, and human behaviour because those pathways often provide faster access than conventional perimeter attacks. Ransomware remains a visible business threat because it combines operational disruption, extortion pressure, and potential data exposure in a single event. At the same time, misconfigured SaaS platforms, exposed credentials, weak privilege controls, and poor MFA enforcement can create silent but material risk.
For Australian organisations, the strategic challenge is also shaped by regulatory expectations. APRA CPS 234 requires entities to maintain information security capability commensurate with vulnerabilities and threats, while the Australian Signals Directorate (ASD) Essential Eight provides a practical uplift path for preventing, limiting, and recovering from cyber incidents. For many CISOs, the challenge is not deciding whether to implement these frameworks, but how to operationalise them against business-critical services without creating unnecessary friction.
A mature strategy treats cyber risk as a system of dependencies, not a set of isolated technical issues. BCyber’s Perfect Storm scenario intelligence capability is designed to test exactly that kind of compound risk—how identity compromise, third-party failure, and incident escalation can intersect under pressure.
Cybersecurity maturity is not proven by the number of tools deployed. It is proven by how well the organisation can maintain trust and continuity when pressure increases.
Cross-functional leadership as a core capability
A CISO rarely succeeds by authority alone. The role depends on influence across finance, legal, HR, operations, procurement, internal audit, and executive leadership. Each function sees risk through a different lens, so the CISO must build a shared language that connects security priorities to business outcomes.
That means understanding commercial objectives, regulatory obligations, workforce realities, and operational constraints. It also means negotiating priorities without turning every conversation into a technical debate. In government, for instance, the discussion may centre on data classification, records retention, and citizen service continuity. In healthcare, it may involve clinical workflow integrity, patient data privacy, and ransomware containment. In financial services, it may focus on privileged access, authentication assurance, and third-party concentration risk.
The strongest CISOs create alignment instead of friction. They help other leaders see that cybersecurity is not competing with the business, but protecting the business’s ability to operate, grow, and recover.
Building a Strategy Around Business Value and Risk Appetite
Knowing what the organisation must protect
A business-aligned strategy starts with asset visibility. The organisation must know which services, data sets, identities, systems, and suppliers are most important to its success. That includes critical business services, sensitive information, privileged access, endpoints, infrastructure, cloud workloads, SaaS applications, and third-party dependencies.
Without that map, security investment becomes generic and uneven. With it, the CISO can direct resources toward the areas where failure would hurt most. This is where BCyber’s GRACE Portal becomes strategically useful: by providing a single dashboard, cross-product analytics, executive reporting, compliance tracking, and real-time monitoring, it centralises the operational picture needed for governance and decision-making.
Criticality mapping is especially useful because it connects technical assets to business functions. A payroll system is not just an application; it is part of workforce trust, financial continuity, and statutory obligations. A patient records platform in healthcare is not just a database; it is a clinical safety dependency. A citizen-facing portal in government is not just a web app; it is an essential public service channel.
This is where self-learning security thinking becomes useful. As the business changes, the knowledge base should grow with it. Asset inventories, dependency maps, and service criticality assessments should not sit as static documents. They should be reviewed, improved, and fed back into governance, so the organisation learns from change rather than being surprised by it.
Defining what matters most to the business
Not every asset deserves the same level of protection, and not every risk has the same business consequence. A practical CISO strategy begins by identifying what the business cannot afford to lose. That may include revenue-generating platforms, safety-critical systems, regulated records, customer trust, or essential service delivery.
Security priorities should then be shaped around those value drivers, not around technical severity alone. A low-visibility technical flaw may be less urgent than a moderate issue that could interrupt a critical service. For instance, a missed patch on an internet-facing server may carry less business impact than a misconfigured identity provider that could expose privileged access across multiple business units.
BCyber’s Profiler behavioral intelligence platform supports this prioritisation by identifying access anomalies, insider threat indicators, and user activity patterns that may not appear severe in isolation but become critical when mapped to business context.
A useful way to frame the executive discussion is to ask three questions:
- What services must continue during disruption?
- What information, if exposed, would create legal, commercial, or trust impacts?
- What downtime or control weakness can the business realistically accept?
Those questions create a bridge between operational reality and strategic planning. They also help security teams stop chasing every issue with equal urgency.
Setting acceptable risk with leadership
Risk appetite is not a security-team opinion; it is a leadership decision. The board and executive team should define how much risk the organisation is willing to carry in pursuit of growth, efficiency, or innovation. The CISO contributes by explaining likely impact, potential scenarios, and control gaps, but the final acceptance of risk belongs to accountable leaders.
This is especially important under APRA CPS 234, where oversight of material security capability and incident preparedness cannot be treated as an IT-only issue. Documented risk tolerance is equally important. It provides practical thresholds for escalation, exception handling, and remediation timelines.
For example, the organisation may accept a short delay in patching low-impact assets, but not prolonged exposure on privileged systems or regulated records. It may allow limited service degradation in a non-critical application, but not in customer-facing delivery. These distinctions help the security team respond proportionately and avoid over-engineering controls where they do not add meaningful value.
The board should also be involved in this process at the right altitude. Boards do not need every technical detail, but they do need assurance that the organisation understands its most material exposures. They need to know how risk is being measured, what remains unresolved, and whether leadership is comfortable with the current position.
Governance, Metrics, and the Discipline of Evidence
Security governance as the operating backbone
Governance is the structure that turns strategy into repeatable action. It defines who decides, who executes, who is consulted, and who is accountable. In cybersecurity, strong governance prevents fragmentation, duplicate effort, and decision drift. It also ensures that policies, standards, and controls are not just written, but actually used in the business.
BCyber’s platform evidence reflects that governance maturity model in practice: 21 policies, 8 processes, and a growing body of 374 knowledge hub entries and 773 published articles. These artefacts support consistent interpretation of controls across business units and help prevent “policy drift” when organisations scale or restructure.
A mature governance model should clearly connect cyber risk to enterprise risk management. That means consistent terminology, regular reporting, and clear escalation pathways to executive and board oversight. In Australian organisations, this alignment is particularly important when working against obligations such as APRA CPS 234, the Privacy Act 1988, and sector-specific healthcare requirements such as the My Health Records Act 2012 and privacy/security obligations surrounding health information.
The aim is not to bolt compliance onto strategy after the fact, but to embed evidence and accountability into the operating model from the start. Policies and standards then become the practical language of governance. Policies set the expectation, standards define the baseline, and controls operationalise the requirement. Frameworks such as NIST Cybersecurity Framework, ISO/IEC 27001:2022, and the ASD Essential Eight should be adapted to the organisation’s actual risk profile.
Measuring what matters to executives and boards
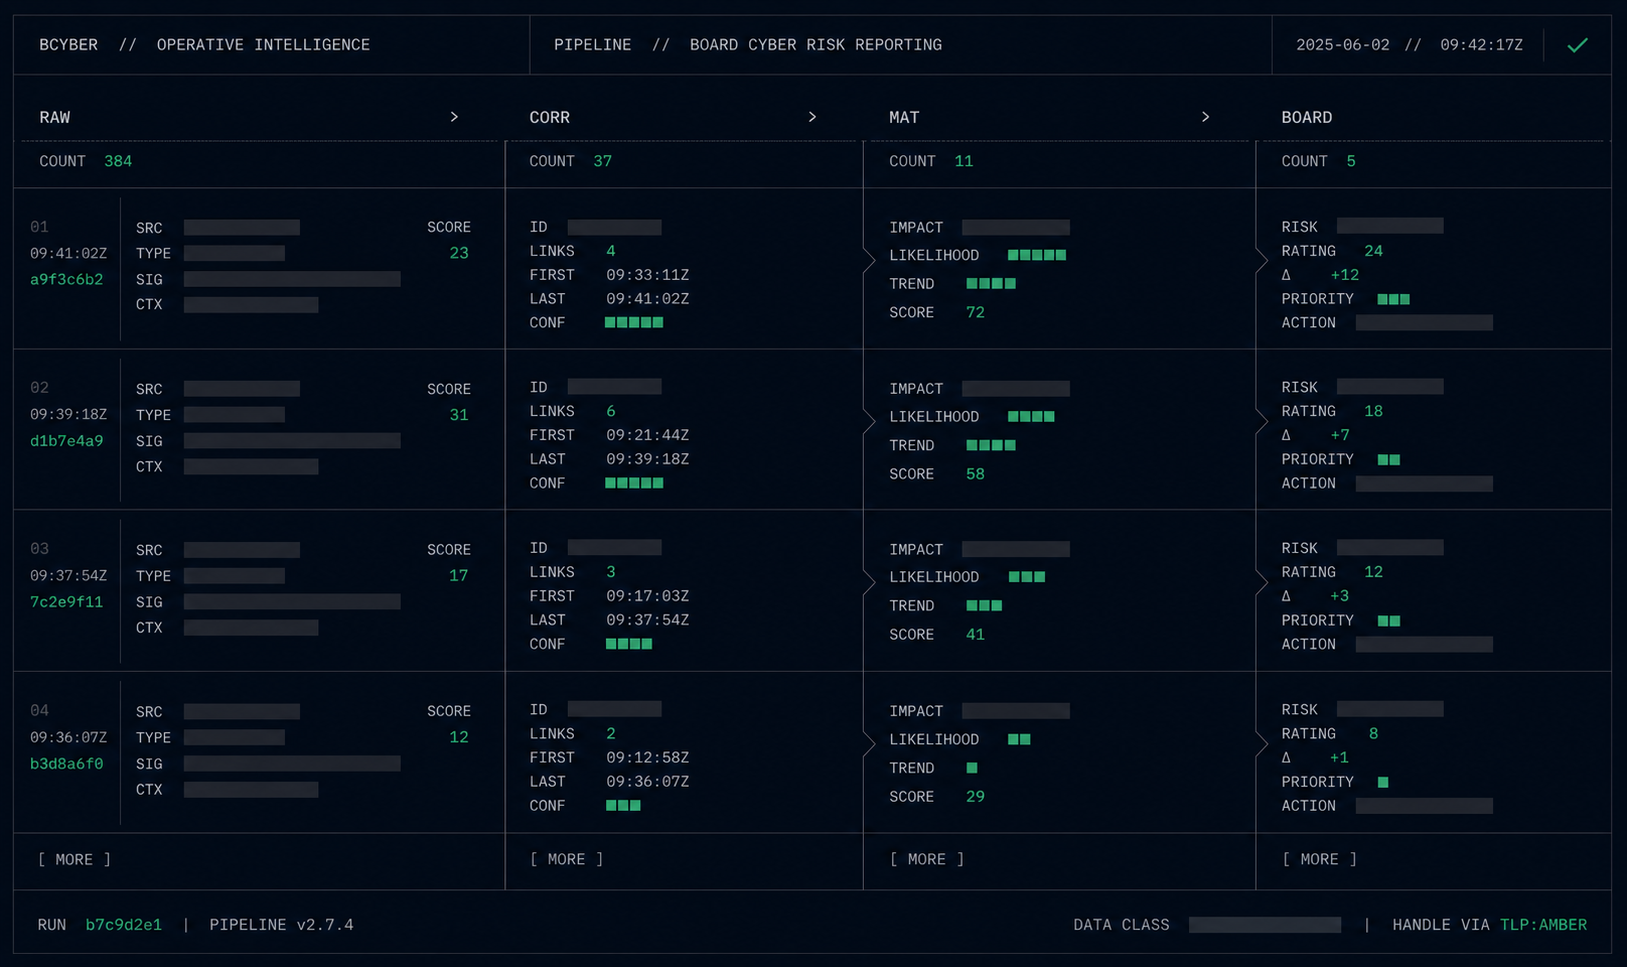
Boards and executives need concise, meaningful reporting that shows whether the organisation is getting safer, more resilient, and more prepared. The best metrics are the ones that reveal business readiness rather than technical noise.
Useful measures include:
- risk posture trends,
- incident frequency and severity,
- mean time to detect and respond,
- control coverage,
- remediation ageing,
- patch compliance against Essential Eight maturity targets,
- and business service resilience indicators.
These should be interpreted in context, not presented as isolated numbers. The goal is to support decision-making, not overwhelm readers with dashboards. BCyber’s GRACE Portal is built for this executive layer through executive reporting and real-time monitoring, while Paradigm supports compliance mapping, policy automation, risk quantification, and GRC automation.
A strong report should answer four questions:
- What has changed?
- What matters most?
- What remains unresolved?
- What decisions are needed?
This structure keeps reporting focused on outcomes and accountability. It also helps the board see whether the cyber program is reducing exposure or simply creating activity.
Avoiding the trap of technical theatre
One of the most common leadership mistakes in cybersecurity is confusing visibility with value. A program can produce many reports, meetings, and dashboards without materially reducing risk. Technical theatre looks busy, but it often leaves the business less certain about its real exposure.
Effective CISOs resist that trap by focusing on material risk, control effectiveness, and measurable improvement. They ask whether each activity changes the organisation’s ability to prevent, detect, respond to, or recover from attacks. This discipline matters because executive attention is limited. If the security function presents too much detail, it risks losing the room before the decision point is reached. If it presents too little, leaders cannot make informed choices.
Leading People, Culture, and Operational Resilience
Leading through complexity and change
The CISO role sits in a space where uncertainty is normal and competing priorities are constant. New threats emerge, business plans shift, and resources remain finite. Effective leaders do not pretend to eliminate uncertainty; they create clarity inside it. They establish priorities, maintain calm during incidents, and keep the organisation focused on what matters most.
This kind of leadership is especially important during change events such as mergers, system migrations, or major control uplift programs. In those situations, the CISO needs reliable assessment data, rapid triage, and repeatable incident workflows. BCyber’s CyberTriage platform supports that need with 4-minute triage, automated response, threat containment, forensic analysis, and incident playbooks.
Adaptability is essential because no strategy survives unchanged for long. A CISO must review assumptions, challenge stale plans, and adjust the roadmap as the environment changes. That includes learning from incidents, assessments, and control failures rather than treating them as isolated problems. Over time, those lessons should reshape governance, training, and technical baselines.
Building a security culture that lasts
Security culture is not a training module; it is the set of everyday behaviours that shape how people handle risk. A strong culture encourages people to report issues early, follow policy consistently, and treat security as part of their role rather than an external burden.
That requires more than awareness campaigns. It requires leaders at every level to model the right behaviour and reinforce the same expectations repeatedly. Culture becomes visible in how people respond to phishing, handle sensitive data, and escalate suspicious activity. BCyber’s 50 courses are designed to support this operational habit-building, and select learning paths align to the GRACE model by reinforcing governance, resilience, assurance, compliance, and executive accountability.
Examples of practical training alignment include:
- Policy awareness and attestation aligned to governance and compliance,
- Incident reporting and escalation aligned to resilience and response,
- Privacy handling and data classification aligned to regulatory assurance,
- Phishing and credential hygiene aligned to identity and behavioural risk.
The CISO also plays a central role in creating a psychologically safe environment for reporting. If staff fear blame, they hide mistakes and delay escalation. If they are encouraged to speak up early, the organisation can intervene sooner and reduce harm. This is particularly important for identity compromise, email misuse, and operational exceptions, where small failures can escalate quickly.
Resilience as a strategic capability
A resilient security program balances prevention, detection, response, and recovery. Prevention reduces obvious exposure, detection shortens dwell time, response limits damage, and recovery restores business functions. If any one of these elements is neglected, the whole model weakens.
This is why resilience must be treated as a strategic capability rather than a recovery exercise after something goes wrong. Business continuity, disaster recovery, and crisis management all belong in the CISO’s strategic sphere. They are not separate administrative tasks, because they determine whether the organisation can continue operating during ransomware, infrastructure failure, or major service disruption.
Recovery plans should be tested regularly and tied to critical services, not generic assumptions. BCyber’s Perfect Storm scenario modelling supports this with resilience testing, impact analysis, and war gaming for compound events. In Australian settings, this also supports obligations under APRA CPS 234, where evidence of preparedness matters as much as stated intent.
Third-party and supply-chain risk also sit inside resilience planning. Many organisations now depend on vendors, managed service providers, and cloud platforms for core operations. A mature CISO strategy therefore includes due diligence, contractual controls, monitoring, and tiered oversight for suppliers based on criticality. The goal is to understand which dependencies could disrupt the business and to make those risks visible before they become incidents.
BCyber’s TopSpin platform adds value here through storage forecasting, trend analytics, capacity planning, cost optimization, and performance monitoring—capabilities that support resilience planning where storage growth, backup windows, and recovery performance are operational constraints.
Preparing the CISO Function for What Comes Next
Adapting to emerging threat models
The threat environment does not stand still, and neither can the security strategy. AI-enabled attacks, faster credential abuse, automation-driven reconnaissance, and identity-centric intrusion methods are changing the shape of risk. These developments do not invalidate the fundamentals, but they do increase the importance of governance, visibility, and rapid adaptation.
A static strategy becomes obsolete quickly if it is not refreshed against new patterns of attack. The CISO must therefore lead a program that learns continuously and updates its assumptions. BCyber’s Paradigm platform is designed for this operating reality through its Synapse AI Engine, risk quantification, policy automation, and compliance mapping capabilities.
The practical response is not to chase every new threat with a separate tool. It is to strengthen the foundations: identity protection, asset visibility, hardened configuration, tested recovery, and reliable reporting. Those capabilities remain valuable even as attack methods evolve. When they are connected to business services and executive oversight, they become durable.
Supporting transformation without losing control
Digital transformation will continue to reshape how organisations deliver value. Cloud adoption, application modernisation, remote work, and SaaS expansion are now standard business patterns, not exceptional events. The CISO must enable these changes without allowing risk to outrun governance.
That is where security-by-design and architecture review become powerful. If security is built into the design process, the organisation avoids expensive retrofits and conflicting decisions later. This also requires close partnership with technology and delivery teams. Security cannot be a late-stage gate that slows progress without explanation. It must be part of the planning conversation from the beginning, helping the business choose architectures that support both speed and control.
This is especially important when adopting new platforms or integrating acquisitions. The better the collaboration, the less likely the organisation is to create hidden exposures during transformation. BCyber’s Privacy in Depth service supports this with comprehensive privacy management for Australian privacy obligations, helping organisations align data handling, retention, and disclosure practices with regulatory expectations.
Leadership skills the future CISO needs
The future CISO skill set will continue to blend technical depth with executive discipline. Business acumen, stakeholder management, crisis leadership, cloud and identity expertise, and data-driven decision-making will matter more than ever. The leaders who thrive will be those who can connect security work to business continuity, customer confidence, and strategic execution.
In that sense, the role is becoming less about guarding a perimeter and more about stewarding an organisation’s ability to adapt safely. That is why BCyber’s leadership and content ecosystem is built around measurable governance, operational learning, and resilient decision-making—supported by real-world implementation data, not abstract claims.
BCyber’s own industry recognition reinforces that position:
- 2025 Finalist Cybersecurity Professional Of The Year — Karen Stephens, Co-Founder & CEO
- 2025 GRC Provider of the Year — Finalist
- 2025 AI Innovator - Cyber Security — Finalist
Regulatory and Framework References for Australian CISOs
For teams building or refreshing a CISO strategy, the following sources are the most relevant starting points:
- APRA CPS 234 – Information Security
- ASD Essential Eight
- ACSC – Strategies to Mitigate Cyber Security Incidents
- NIST Cybersecurity Framework
- ISO/IEC 27001:2022
- OAIC – Australian Privacy Principles
- My Health Records Act 2012
Key Takeaways
A modern CISO strategy begins with clarity about what the business must protect and what it can afford to lose. It then uses governance, evidence, and clear decision rights to align security work with enterprise risk and operational priorities. The strongest leaders communicate in business terms, build trust across functions, and make resilience measurable rather than theoretical.
They also recognise that culture, talent, and recovery capability are not side projects; they are central to sustained protection. Most importantly, they treat cybersecurity as a living discipline that learns, adapts, and improves alongside the organisation itself.
Disclosure: This whitepaper includes references to BCyber products, services, and platform data for illustrative and educational purposes. Where examples are drawn from BCyber client environments, they are presented in aggregated and de-identified form. No confidential client information has been disclosed.