Board Cyber Risk Reporting: How to Turn Technical Security Data into Board-Level Decisions
By BCyber Security Team | CISSP, CISM Last updated: 23 September 2026

Board cyber risk reporting is the discipline of turning technical security activity into evidence a board can use to govern, prioritise, and challenge management. If you sit on a board, or report to one, the question is not whether the dashboard is full, but whether it helps directors decide what matters, what has changed, and what needs to happen next.
In Australian organisations, that distinction matters because cyber risk now sits alongside financial, operational, legal, and reputational risk. Good reporting does not bury directors in alerts, ticket counts, or tool names; it gives them a clear line of sight to business impact, control performance, and residual exposure.
At BCyber, we see this across client fact-find assessments, board packs, and assurance programs. Across our platform inventory of 23 policies, 9 processes, 50 courses (2 enrollments), 939 published articles, 530 knowledge hub entries, 11 clients, and 14 fact-find assessments, the consistent theme is simple: boards need fewer metrics, but better evidence.
What board cyber risk reporting actually is
A governance tool, not a technical dump
Board cyber risk reporting is the structured communication of an organisation’s cyber risk posture to directors and senior executives. It exists to support governance, oversight, and strategic decision-making, not to document every patch, scan, or alert.
A board needs to understand exposure, control effectiveness, risk movement, and the actions management is taking in response. That means the report should answer the hard questions in plain language, rather than assume the board can translate logs into business consequences. If the report cannot do that, it is likely reporting activity rather than risk.
BCyber’s GRACE Portal is designed for that board-level view: Single Dashboard, Cross-product Analytics, Executive Reporting, Compliance Tracking, and Real-time Monitoring. In practice, the most useful board reports typically combine GRACE outputs with governance artefacts from Paradigm for GRC automation and Perfect Storm for scenario intelligence, so directors can see not only what happened, but what could happen next.
Why it differs from operational security reporting
Operational reporting is useful, but it serves a different audience. Security teams need tickets, alerts, patch queues, detection tuning, and incident workflows to run the program day to day. Boards need a smaller set of signals that describe the business meaning of those operational facts.
The same dataset may feed both reports, but the framing must change completely. One report helps engineers act; the other helps directors govern.
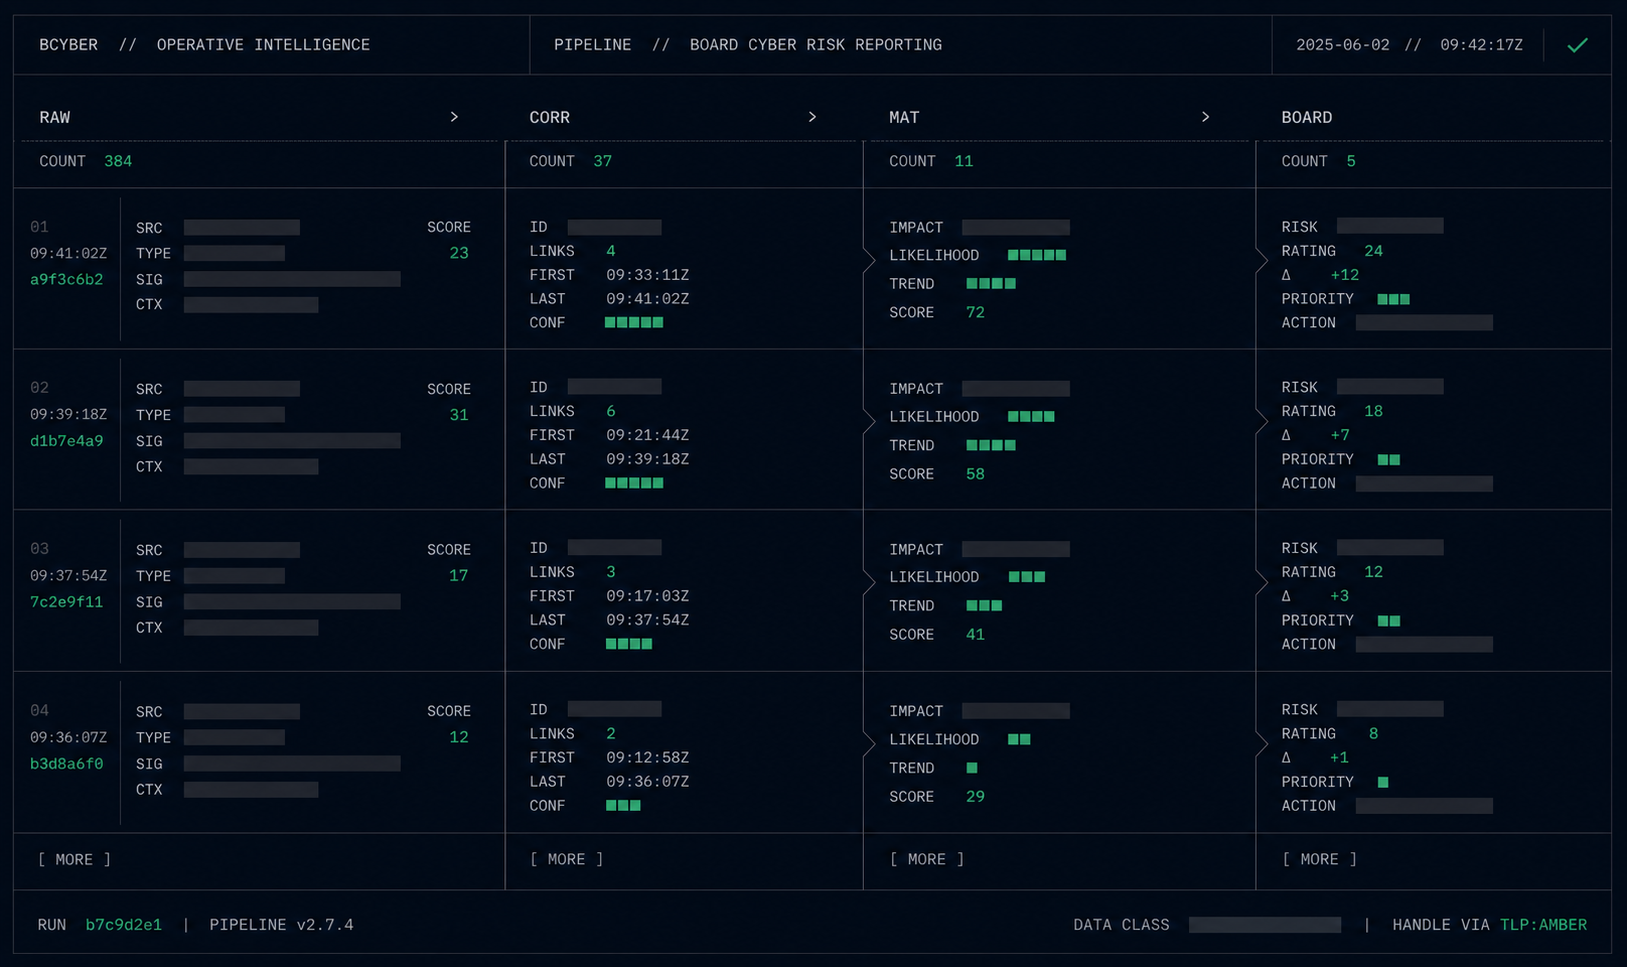
A useful way to think about the difference is this: operational reporting answers “what happened?” while board reporting answers “so what?” and “what now?”. For example, a list of 412 overdue vulnerabilities tells a board very little on its own. A report that identifies the 12 vulnerabilities affecting customer-facing systems, explains the likely business impact if exploited, and shows whether remediation is blocked by dependency or funding is far more useful.
This is where technical depth matters. Mature board reporting usually includes:
- risk rating methodology aligned to ISO 27005 or enterprise risk appetite,
- control effectiveness evidence mapped to ISO/IEC 27001:2022 Annex A,
- maturity or uplift indicators aligned to the ACSC Essential Eight, and
- incident metrics grounded in NIST SP 800-61 incident lifecycle language.
That is the shift from noise to decision support.
What a board report should answer
A board-ready cyber report should answer a short set of questions clearly and consistently:
- What matters most right now?
- What has changed since the last report?
- What evidence supports the current assessment?
- What decisions or approvals are needed now?
A board report that does not support a decision is often just a record of effort, not a report of risk.

Why boards need cyber risk in business language
Cyber risk is already an enterprise risk
Cyber incidents can stop operations, interrupt service delivery, damage trust, trigger regulatory scrutiny, and create financial loss. In Australia, that intersects with obligations under the Privacy Act 1988, the Essential Eight, APRA CPS 234 for regulated entities, and sector-specific obligations in areas such as health and critical infrastructure.
For many boards, the challenge is not whether cyber matters, but whether it is being presented in a form that supports real oversight. A board cannot govern what it cannot interpret. That is why cyber reporting must be translated into business terms.
In a financial services environment, for example, a privileged access failure might expose payment platforms or customer records; in healthcare, the same issue may affect clinical systems, patient privacy, and continuity of care; in government, it may compromise citizen data and service delivery. The risk changes by sector, but the governance need is the same: directors need to know whether the organisation can resist, respond, and recover.
Visibility matters more than volume
A longer report is not necessarily a better report. Too much detail can hide the few issues that matter most. Boards need concise, prioritised insight that reflects material risks, not a flood of low-value status updates.
Strong board reporting uses selective disclosure. It surfaces the handful of risks that could materially affect operations, compliance, finances, or reputation, then gives enough context for a board to challenge management. It also avoids vanity metrics that look healthy but do not demonstrate resilience.
A high phishing training completion rate, for instance, is useful, but only if it is paired with evidence that user behaviour is improving and that privileged accounts are better protected. BCyber’s 50 courses and 2 enrollments are most useful when the board can see how training is mapped to control uplift, human-factor risk reduction, and policy adherence—not merely completion.
Governance improves when reporting is useful
Good reporting creates better governance because it gives directors something concrete to discuss, question, and approve. It also makes management more accountable for the risks they own.
When the report shows ownership, due dates, blockers, and progress, the conversation becomes more disciplined. That makes it easier to distinguish a genuine risk treatment problem from a resource problem, a dependency problem, or a decision that has simply been deferred.
This matters because cyber risk is rarely isolated to the technology function. It often involves procurement, legal, HR, operations, finance, and business leadership. A board-ready report should make those relationships visible. If a supplier issue is delaying remediation, or a business unit is accepting risk without documenting it, that should be obvious.
BCyber’s Paradigm platform is built to support this governance layer through GRC Automation, Synapse AI Engine, Risk Quantification, Policy Automation, and Compliance Mapping. For boards, that is especially helpful when risk treatment decisions need to be tracked against policy obligations, control owners, and enterprise risk appetite.
What directors actually need to see
Exposure, control effectiveness, and movement over time
Directors need a clear picture of exposure. That means understanding which critical systems, sensitive datasets, suppliers, and business processes are most at risk. It also means identifying where a compromise would cause the greatest business impact, not just where the most technical weaknesses exist.
A small number of weaknesses in a high-value environment can matter more than a long list of minor issues elsewhere. Board reporting should reflect that reality instead of flattening it into one score.
Control effectiveness is the second essential lens. Boards should know whether key safeguards are designed well and operating as intended, especially around identity, backups, segmentation, detection, and response. The difference between “implemented” and “working” matters a great deal.
For example:
- MFA may be enabled, but not enforced for privileged accounts or contractors.
- Backups may exist, but restore testing may fail recovery time objectives (RTOs).
- EDR may be deployed, but telemetry may be incomplete on OT or legacy systems.
- Segmentation may exist on paper, but lateral movement may still be possible due to shared admin pathways.
This is where evidence matters most. Control statements should be supported by testing results, assurance findings, incident learnings, or independent review where possible. Where evidence is incomplete, the report should say so.
Risk movement over time is the third part of the picture. A board needs to know whether cyber risk is rising, falling, or shifting shape. That requires trend reporting, not just point-in-time status.
Material incidents and near misses
A board report should include material incidents and near misses, but only in a way that supports governance. The point is not to relive every technical detail. The point is to show what happened, the likely impact, how it was contained, what lessons were learned, and what is being changed as a result.
Near misses matter because they can expose weak controls before a larger event occurs. In a mature reporting culture, near misses are treated as evidence, not embarrassment.
This is where CyberTriage can be valuable operationally and at the governance layer. Its 4-Minute Triage, Automated Response, Threat Containment, Forensic Analysis, and Incident Playbooks capabilities help security leaders compress response time, which directly affects what the board later sees in terms of materiality, containment success, and recovery trajectory.
Residual risk and accepted risk
Residual risk is the risk that remains after controls are applied. That is what the board ultimately needs to understand, because no control removes risk entirely.
A useful report should show what risk remains, why it remains, and who has accepted it. If the accepted risk sits outside appetite, or if there is no documented decision, the board should be able to see that gap. This is a governance issue, not just a security issue.
Risk acceptance should never be implied by inaction. If remediation is delayed because the work is complex or funding is unavailable, that needs to be visible. If a business owner has chosen to accept the exposure temporarily, that decision should be traceable.
BCyber’s Profiler platform is particularly relevant here because behavioural risk often sits behind residual exposure: Behavioral Analysis, Insider Threat Detection, Access Pattern Monitoring, Risk Scoring, and User Activity Analytics help identify whether people, access paths, or anomalous behaviour are driving the remaining risk.

Real-world scenarios that change how boards should read the report
Financial services: CPS 234 and privileged access exposure
A registered financial services entity may report that privileged access reviews were completed on time. That may sound positive, but the board should ask:
- Were the reviews risk-based or just calendar-based?
- Were dormant privileged accounts disabled?
- Was cloud admin access included?
- Were exceptions approved and time-limited?
Under APRA CPS 234, directors are expected to see whether information security capability is commensurate with threats and vulnerabilities. In practice, that means board reporting should show the effect of identity and access decisions on critical business services, not just policy compliance.
Healthcare: patient safety and ransomware readiness
A healthcare provider can have “green” patch metrics and still be underprepared if clinical systems cannot be restored in sequence after an outage. The board should want to know whether backups are immutable, whether restore tests include electronic medical record systems, and whether downtime procedures have been rehearsed with clinical leaders.
Here, reporting should connect cyber to patient safety, service continuity, and privacy obligations. That makes the report more useful to directors who oversee both risk and service quality.
Government: service availability and citizen data
In government, cyber reporting should distinguish between confidentiality, integrity, and availability impacts across digital services. A supply chain weakness in a hosted environment may not only expose records; it may interrupt benefit processing, permit data tampering, or affect trust in public services.
Directors in government and adjacent agencies should expect reporting to reference control testing, third-party assurance, and incident response coordination, especially where whole-of-government dependencies exist.
What strong reporting looks like in practice
An executive summary that leads with the material issues
A strong board report starts with the top three to five issues that matter most, not a generic narrative. Those issues should be stated in business language and linked to impact.
If a major identity weakness affects privileged access, say so directly. If backup restoration cannot yet meet recovery expectations, explain the business consequence. The summary should also identify whether the board is being asked to note, approve, challenge, or decide something specific.
This section works best when it is concise and comparative. Directors should be able to see what changed since the last report and why it matters.
Metrics that show movement, not just totals
Good metrics measure change, concentration, and performance over time. They do not simply count what exists. A useful board report might show:
- overdue critical vulnerabilities affecting key systems,
- the outcome of backup recovery tests,
- third-party assurance status,
- privileged access exceptions,
- phishing susceptibility trends,
- incident response readiness, and
- risk acceptance aged beyond tolerance.
The point is to show whether resilience is improving and where weaknesses are clustering. Trend lines matter because they reveal direction, not just volume.
Control maturity and real-world effectiveness
Boards often hear that a control is “implemented”, but implementation is not the same as effectiveness. A strong report should separate design from performance.
For example:
- MFA may be deployed, but is it enforced for privileged accounts, remote access, and critical third parties?
- Backup systems may exist, but are they routinely restored and validated against recovery objectives?
- Detection tools may be deployed, but are they tuned to reduce blind spots and alert fatigue?
This is where evidence matters most. Control statements should be supported by testing results, assurance findings, incident learnings, or independent review where possible. Where evidence is incomplete, the report should say so.
Ownership, actions, and blockers
A board report should make ownership unmistakable. Every material risk and remediation item should have a named owner, a due date, current status, and a note on any blocker.
If action depends on funding, procurement, a vendor fix, or a business decision, that should be visible. Otherwise, risks can appear to be “in progress” for months without meaningful movement. Directors need to know whether management is reducing risk or simply reporting activity against it.
BCyber’s GRACE Portal helps bring this into one view with executive reporting, while TopSpin adds Storage Forecasting, Trend Analytics, Capacity Planning, Cost Optimization, and Performance Monitoring—useful where storage resilience, ransomware recovery, or archive growth create governance decisions that affect recovery readiness and budget.
How organisations can improve board reporting without adding noise
Start with the decision, then build the report around it
The easiest way to improve board reporting is to start with the decision the board needs to make. Then work backwards to the evidence that supports that decision. This forces the report to become selective and relevant.
If the board needs to approve a remediation investment, the report should show the risk being reduced, the options considered, the cost of inaction, and the evidence behind the recommendation. That is much stronger than a status dashboard with no destination.
A practical reporting structure can help. Many organisations benefit from a repeating sequence:
- risk summary,
- what changed,
- evidence,
- decisions required, and
- actions in flight.
That rhythm makes reports easier to follow and compare over time. It also supports better challenge because directors know where to find the answer they need.
Align cyber reporting with enterprise risk
Cyber reporting should not live in a separate universe. It needs to connect to the organisation’s broader enterprise risk framework, risk appetite, and governance cycle. That means aligning terminology, escalation thresholds, and ownership models.
It also means feeding cyber findings into the wider risk register in a way the board can compare with other strategic risks. When that happens, cyber becomes part of the organisation’s normal governance rhythm rather than an annual compliance event.
In Australian contexts, that alignment can support obligations under:
- APRA CPS 234
- Privacy Act 1988
- ASD Essential Eight
- relevant sector guidance and reporting obligations
For organisations using BCyber’s Privacy in Depth capabilities, this is especially relevant where privacy risk, not just cyber risk, is a board concern—particularly in environments governed by the Australian Privacy Principles and breach notification obligations.
Use evidence, and publish the limits
The strongest reports do not pretend certainty where none exists. They show evidence, explain assumptions, and name limitations. If a report relies on partial testing, it should say so. If a metric is derived from a tool that has blind spots, that limitation should be visible.
If a control is working in one environment but not another, the report should not flatten that difference into a single green status. In a market full of polished dashboards, plain limits are a sign of maturity.
The most trustworthy report is not the one that knows everything. It is the one that shows its sources and admits what it does not yet know.
This approach also supports a living knowledge base, where the organisation’s understanding compounds over time. Every report becomes a learning asset rather than a one-off artefact. Signals from incidents, assurance activities, and remediation efforts should inform the next board cycle, not vanish after the meeting.
Where BCyber’s platforms fit in board reporting
BCyber’s product ecosystem is designed to support different layers of cyber governance:
- GRACE Portal for unified executive visibility and board reporting,
- Paradigm for AI-driven governance, risk, and compliance automation,
- Profiler for behavioural intelligence and insider-risk insight,
- TopSpin for forecasting and capacity planning,
- CyberTriage for incident response acceleration,
- Perfect Storm for scenario modelling and resilience testing,
- Privacy in Depth for privacy management and compliance support.
For board reporting, the key is not the tool itself; it is the evidence chain the tool enables. A board can challenge management more effectively when metrics are linked to:
- policy coverage,
- process maturity,
- control testing,
- incident outcomes,
- risk acceptance decisions, and
- compliance mappings.
BCyber’s content library—939 published articles and 530 knowledge hub entries—supports this evidence-led approach by helping teams build repeatable reporting language around governance, control effectiveness, and resilience.
BCyber recognition and credibility
BCyber’s governance and AI capabilities have also been recognised through industry nominations, including:
- 2025 Finalist Cybersecurity Professional Of The Year — Karen Stephens, Co-Founder & CEO
- 2025 GRC Provider of the Year — Finalist
- 2025 AI Innovator - Cyber Security — Finalist
These recognitions do not replace evidence in a board report, but they do indicate that the approach is being developed and reviewed in the context of current industry practice.
Verification and trust statement
Verification note: The BCyber platform statistics and product capability references in this article are based on real BCyber-provided platform data supplied for editorial enhancement. They should be verified against current internal product documentation, client statements, and official capability briefs before use in external legal, procurement, or regulatory materials.
Potential bias/conflict note: This article references BCyber products and services for editorial context and may reflect a vendor perspective. Readers should validate claims against independent assurance evidence, internal control testing, and applicable regulatory guidance before adopting any reporting approach.
Conclusion
Board cyber risk reporting is not about generating more slides or more data. It is about producing clearer decisions, better governance, and a more honest view of exposure.
Directors need to know what matters most, what has changed, what evidence supports the current position, and what action is required now. When reports are written in business language, tied to material risks, and supported by evidence, they become useful for oversight instead of decorative for meetings.
The best reports are concise, comparative, and decision-ready. They separate exposure from control effectiveness, surface movement over time, and make ownership unmistakable. They also resist the temptation to hide uncertainty behind polished dashboards. For Australian organisations navigating APRA expectations, privacy obligations, and Essential Eight uplift, that honesty is not a weakness. It is the basis for defensible oversight and better security judgement.
Key Takeaways
- Board cyber risk reporting should help directors govern risk, not inspect technical activity.
- The most useful reports answer what matters, what changed, what evidence supports it, and what decisions are needed.
- Directors need visibility into exposure, control effectiveness, risk movement, material incidents, and accepted risk.
- Plain language, trend reporting, and clear ownership make reports more decision-ready.
- Honest reporting of evidence and limits builds trust and supports stronger oversight over time.
Sources and further reading
- Australian Signals Directorate (ASD), Essential Eight: https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/essential-eight
- APRA, CPS 234 Information Security: https://www.apra.gov.au/information-security-cps-234
- Australian Cyber Security Centre (ACSC): https://www.cyber.gov.au/
- NIST, Cybersecurity Framework 2.0: https://www.nist.gov/cyberframework
- NIST SP 800-61 Rev. 2, Computer Security Incident Handling Guide: https://csrc.nist.gov/publications/detail/sp/800-61/rev-2/final
- ISO/IEC 27001:2022 overview: https://www.iso.org/standard/27001
- Office of the Australian Information Commissioner (OAIC), Australian Privacy Principles: https://www.oaic.gov.au/privacy/australian-privacy-principles